HIPAA Security Rule update

    Enterprise SIEM · Professional and up

    A healthcare SIEM that watches every workstation, and keeps the proof.

    Live Compliance runs an enterprise SIEM on every workstation in your organization, catches what documentation cannot, and files the audit logs, access records, and integrity checks the HIPAA Security Rule asks for, inside the same platform as your policies and training.

    Talk to a Specialist

    10 minutes · No credit card · No call required

    Included on Professional and Enterprise with Detect & Respond, organization-wide encrypted email, Asset Manager, and the Credential Tracker. Nothing is an add-on.

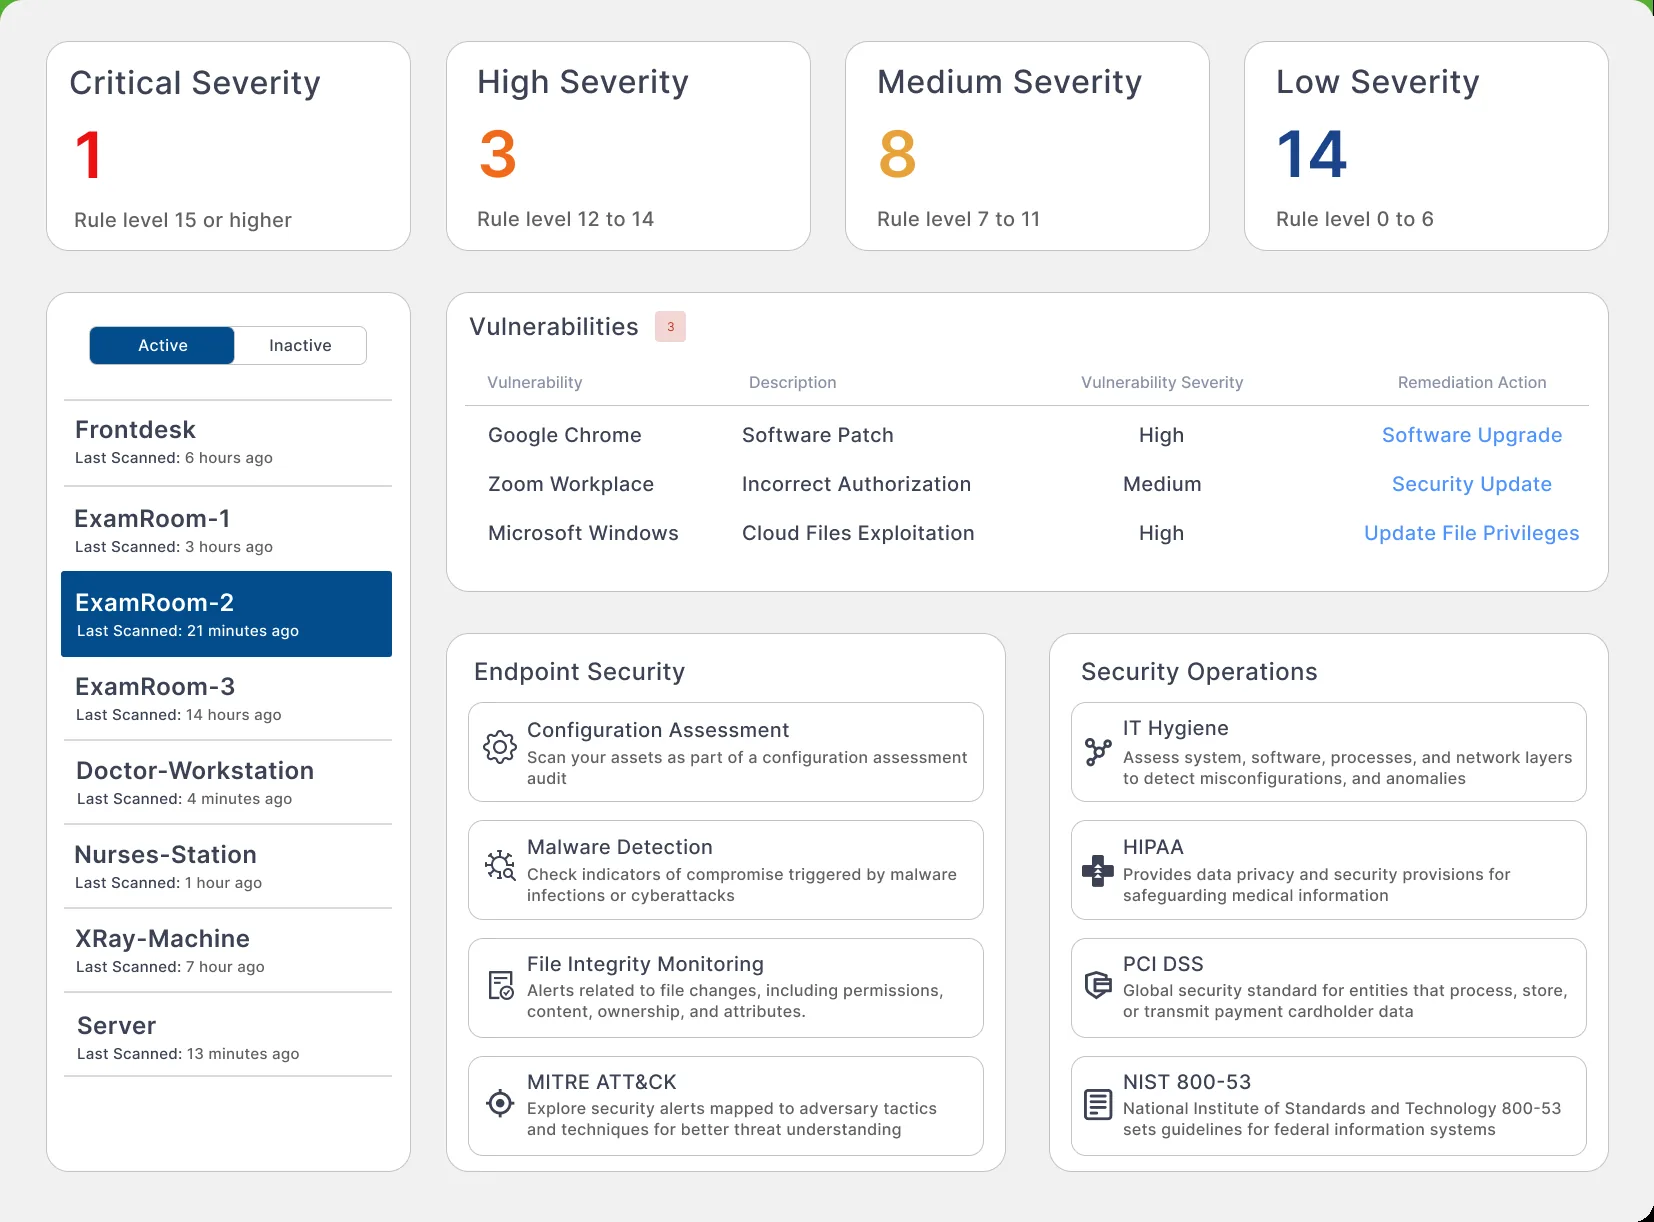
    The Live Compliance security operations screen: findings counted by severity, every workstation with its last scan time, a vulnerabilities table with remediation actions, and the endpoint security and security operations checks.

    Rated by severity, critical first

    Inside the module

    What it watches, and what it proves.

    Two chapters on one real screen, from a demo organization.

    01 / 02

    Watch.

    Every workstation, not a sample.

    An agent on each machine reports in around the clock: the front desk, every exam room, the doctor’s workstation, the nurses’ station, the X-ray machine. A machine that stops reporting is flagged, and nothing depends on someone remembering to run a scan.

    Six checks, on every machine

    • Configuration against benchmarks
    • Malware indicators
    • File integrity
    • Vulnerabilities, severity scored
    • Log analysis
    • Response actions
    The workstation list on the security screen: front desk, exam rooms, the doctor’s workstation, each with the time it was last scanned, beside the vulnerabilities table.

    Scanned 21 minutes ago, like every other machine

    02 / 02

    Prove.

    The technical safeguards, evidenced as they happen.

    The Security Rule asks for audit controls, access monitoring, integrity controls, and transmission security. Each finding is logged with the machine, the severity, and the fix, so the report an auditor reads is the record the platform already keeps.

    How an audit reads the record
    The vulnerabilities table with severity and remediation actions, above the endpoint security checks and the security operations checks, including the HIPAA mapping.

    Logged with the machine, the severity, and the fix

    Detect & Respond keeps each finding in front of you until it is closed, and continuous vulnerability monitoring scores every finding by the likelihood it is exploited, so the critical one comes first.

    In the price

    Included on Professional, not sold beside it.

    A standalone SIEM for a 20-person practice runs $240 to $420 a month before anyone reads an alert. On Professional it is included, with Detect & Respond, organization-wide encrypted email, Asset Manager, and the Credential Tracker, plus $8.33 per employee per month, billed annually, and no add-on fees.

    See the plans
    Essentials
    $399a month
    Single-location practices and business associates
    Professional
    $895a month
    Organizations that want the security layer built in
    Enterprise
    $1,450a month
    Multi-location practices and health systems

    Straight answers

    Healthcare SIEM, in plain words.

    Live Compliance Enterprise SIEM is the security information and event management layer built into the Live Compliance platform: an agent on every workstation, continuous vulnerability monitoring, and the audit evidence the HIPAA Security Rule requires, included on Professional and Enterprise.

    One of 19 modules, sharing a platform with the policies, training, and risk assessment an audit reads beside it.

    • Professional and up
    • Every workstation
    • 500+ organizations
    • Since 2010
    • 100% audit success rate

    A SIEM, security information and event management, collects the security events from every workstation, correlates them, and keeps the record. In healthcare it is how a breach is detected before it becomes a notification, and how the audit logs the HIPAA Security Rule requires get produced. Live Compliance builds the SIEM into the compliance platform rather than selling it beside one.

    It produces the evidence for the safeguards the Security Rule names. Audit controls, through continuous event logging on every workstation. Access monitoring, through authentication and access alerts. Integrity controls, through file integrity monitoring. Transmission security is covered on the same plan by organization-wide encrypted email. Your risk assessment and policies live in the same platform, so the technical evidence and the administrative record are read together.

    Every workstation with the agent installed: configuration against security benchmarks, malware indicators, file integrity, software vulnerabilities scored by severity, and system and application logs, with response actions when a finding needs one. Each machine shows its last scan time, and a machine that stops reporting is flagged as inactive.

    Findings land in the platform on the machine they came from, with the time, the severity, and the recommended remediation. Your named compliance team sees the same view you do, and Detect & Respond keeps each finding in front of you until it is closed, with the record of what was done.

    Nothing beyond the plan. Enterprise SIEM is included on Professional at $895 a month and Enterprise at $1,450, plus $8.33 per employee per month, billed annually, with no add-on fees. Licensed separately, a SIEM for a 20-person practice typically runs $240 to $420 a month, and the whole security layer roughly $870 to $1,250.

    A continuous event log for every workstation, vulnerability findings with severity and remediation status, file integrity and configuration results, and reports that map each of them to the safeguard they evidence. Because the SIEM shares a platform with your risk assessment, policies, and training records, an auditor reads the technical evidence and the administrative record side by side.

    See where your program stands before an auditor does.

    Get your free 10-minute audit-readiness score. Then, if you want it, the guarantee: audit-ready in 60 days, or we keep working at no additional cost until you are.

    Or talk to a specialist

    ~10 minutes · No credit card · No call required

    500+
    healthcare organizations
    100%
    audit success rate
    2010
    protecting healthcare since