HIPAA Security Rule update

    Already have an IT provider

    Already have an IT provider or MSP? Live Compliance works with them.

    Live Compliance does not replace the MSP or IT provider you already use. MSPs use Live Compliance alongside the stack they already run. The platform is the HIPAA program and the security operations an audit examines, sitting next to the people who keep your network up.

    Talk to a Specialist

    10 minutes · No credit card · No call required

    A named compliance team is included on every plan. Specialist support is not a competitor add-on and not reserved for Enterprise.

    The Live Compliance security operations screen: findings counted by severity, every workstation with its last scan time, and a vulnerabilities table with remediation actions.

    The watch your MSP does not have to own

    How the work splits

    An existing MSP is a reason to use Live Compliance, not a reason to skip it.

    IT keeps the environment running. The HIPAA program still needs an owner, a record, and the security operations an auditor reads beside the policies.

    1. 01 · Your MSP

      They keep the network up.

      Your MSP or IT provider keeps workstations, backups, patches, and tickets running, on the tools they already chose. That work stays theirs. Live Compliance does not take it over.

    2. 02 · Live Compliance

      We run the HIPAA program.

      Live Compliance runs the risk analysis, policies, training, vendor agreements, and the security operations an audit examines: SIEM, dark web monitoring, phishing simulation, and encrypted email, with a named compliance team on every plan.

    3. 03 · Together

      The two sit side by side.

      Your MSP does not have to become a compliance team. Live Compliance does not replace IT. MSPs use Live Compliance alongside their stack because it gives healthcare clients a program they can point to, without replacing the relationship they already have.

    What still needs an owner

    SIEM inside the compliance record is not only for shops with no IT.

    The bundle is complementary to an MSP relationship. It is how the technical safeguards and the administrative record get read together.

    01 / 02

    The gap.

    Paperwork platforms still leave a security-ops hole.

    When a documentation-only platform leaves SIEM, phishing defense, dark web monitoring, and encrypted email to whoever handles security, that work often sits outside the compliance record. Your MSP may monitor the network. They rarely own the HIPAA evidence an auditor asks to see next to the policies.

    How the SIEM keeps the proof
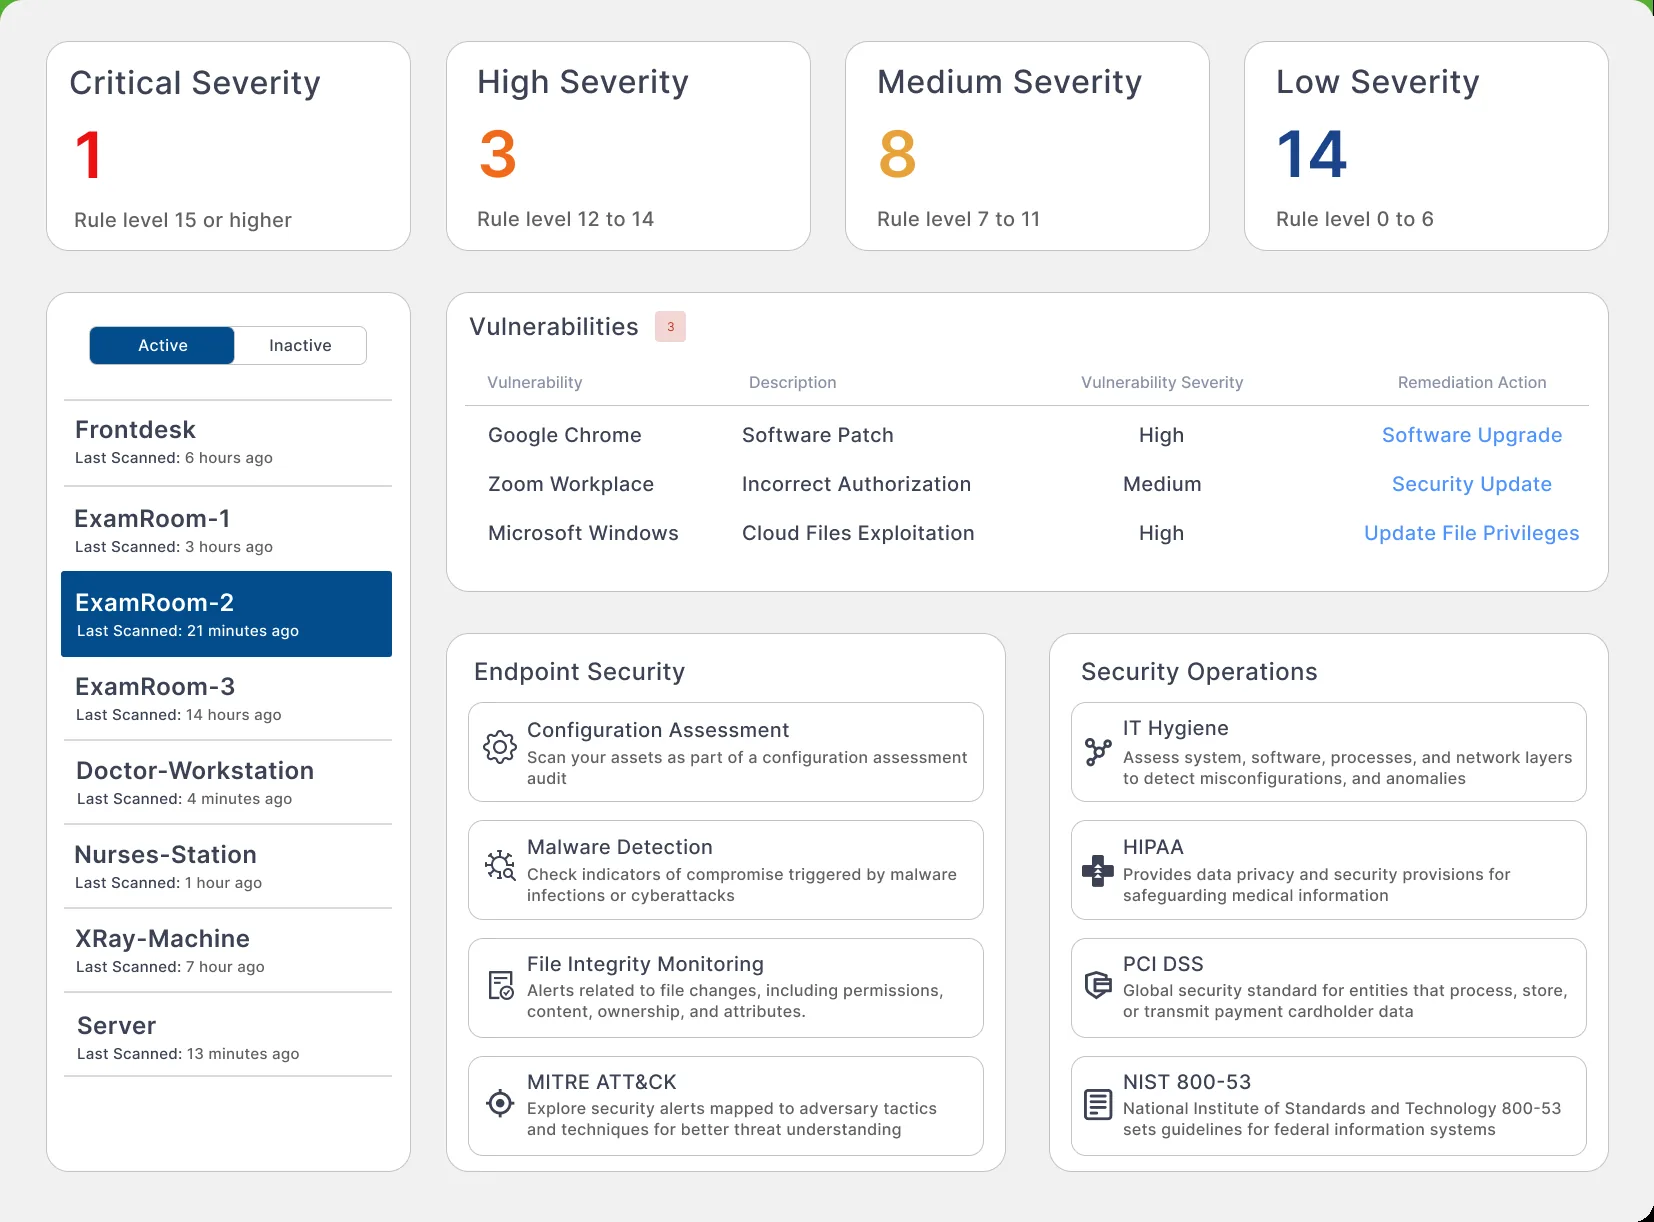
    The Live Compliance security operations screen: every workstation with its last scan time, beside a vulnerabilities table with remediation actions.

    Logged with the machine, ready for the audit

    02 / 02

    The team.

    A named compliance team, on every plan.

    Specialist support is included. A named compliance team guides onboarding, works through findings, and keeps the program alive. That is not a Compliancy Group-only add-on, and it is not reserved for Enterprise. It is on Essentials, Professional, and Enterprise.

    How the Staff Portal names the team
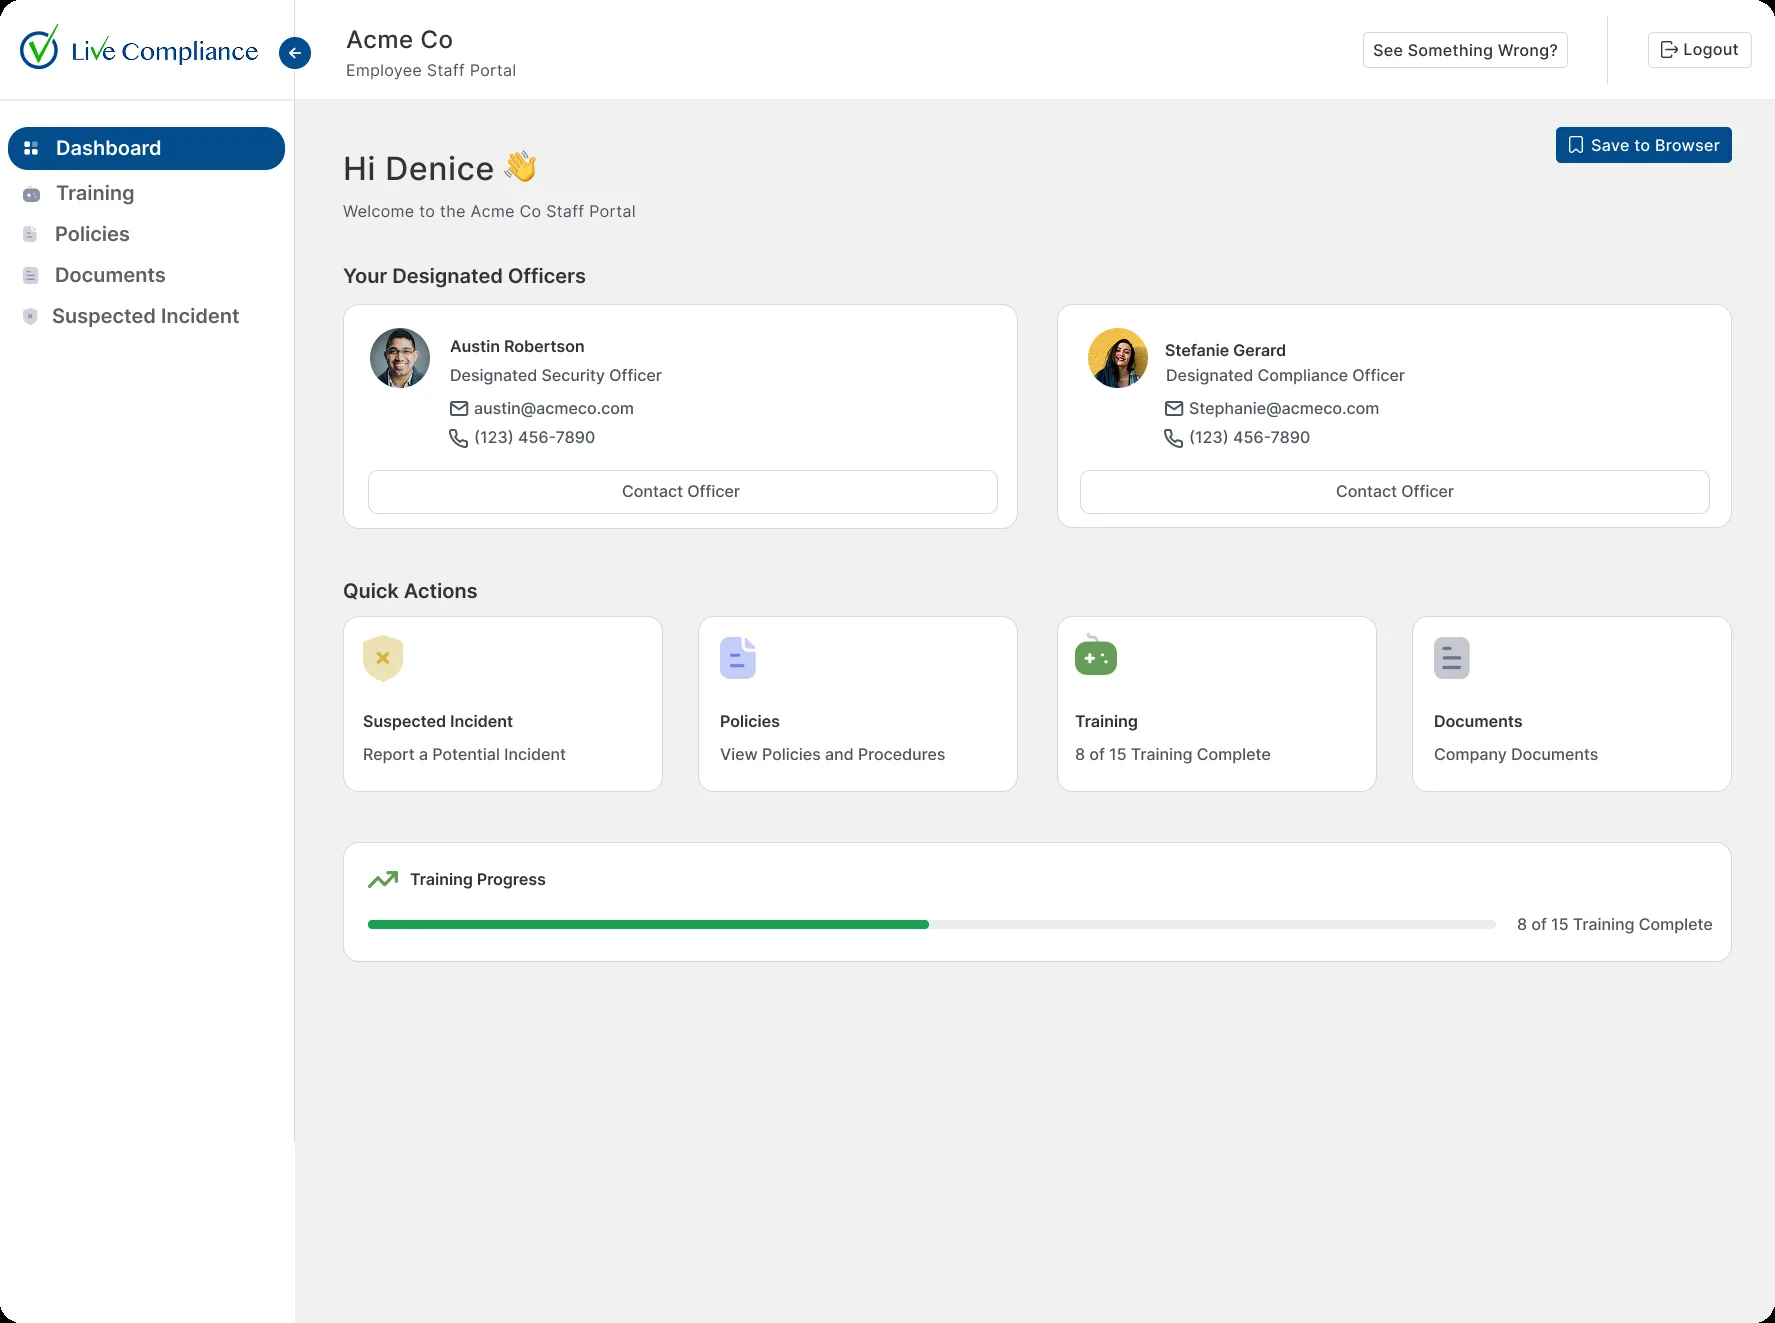
    The Live Compliance Staff Portal: designated security and compliance officers with photos, contact buttons, and the training and policies each employee owes.

    Named officers, in front of every employee

    If this is you

    You already have an MSP, and someone told you a compliance platform with security operations would be redundant.

    That reading is wrong for the organizations Live Compliance is built for. An existing IT relationship does not close the security-ops gap an audit examines, and it does not give you a named compliance team. Live Compliance is the fit even when IT is already covered.

    Accurate as of 17 September 2026. Not legal advice. Verify current requirements for your organization.

    Straight answers

    Live Compliance and your MSP, in plain words.

    Live Compliance works with the MSP or IT provider you already have. It does not replace them.

    MSPs use Live Compliance alongside the stack they already run. A named compliance team is included on every plan. The SIEM and security operations inside the platform are complementary to that IT relationship, not a reason to skip the program.

    • Works with your MSP
    • Named team included
    • 500+ organizations
    • Since 2010
    • 100% audit success rate

    No. Live Compliance does not replace the MSP or IT provider you already use. It works with them. Your MSP keeps the network, backups, patches, and tickets. Live Compliance runs the HIPAA program and the security operations an audit examines, with a named compliance team included on every plan.

    No. An existing SIEM or MSP security stack does not make Live Compliance a redundant cost for the organizations it is built for. The SIEM inside Live Compliance sits in the same record as the risk analysis, policies, and training an auditor reads together. That is complementary to the tools your MSP already runs, not a reason to skip the program.

    Yes. Managed service providers partner with Live Compliance and use it alongside the stack they already run. They stay the IT relationship. Their healthcare clients get the HIPAA program, the named compliance team, and the security operations an audit examines, without the MSP having to become a compliance department.

    Yes, on every plan. A named compliance team guides onboarding, works through findings, keeps the program on track, and answers regulatory questions, with no hourly billing. Specialist support is included on Essentials, Professional, and Enterprise. It is not a Compliancy Group-only add-on and not reserved for a higher Live Compliance tier.

    Documentation-only platforms cover policies, training, and risk assessment, and leave SIEM, phishing defense, dark web monitoring, and encrypted email outside the compliance record. An MSP may monitor the network. They rarely own that HIPAA evidence. The gap stays yours unless the security operations live in the same program as the paperwork.

    Yes. That is the intended setup. A specialist reads what you already have, including the IT relationship, and sets the pace around it. Existing policies, training records, agreements, and assessments import, so nothing restarts. The guarantee stands behind the program: audit-ready in 60 days, or we keep working at no additional cost until you are.

    See where your program stands before an auditor does.

    Get your free 10-minute audit-readiness score. Then, if you want it, the guarantee: audit-ready in 60 days, or we keep working at no additional cost until you are.

    Or talk to a specialist

    ~10 minutes · No credit card · No call required

    500+
    healthcare organizations
    100%
    audit success rate
    2010
    protecting healthcare since